


SUPPORT
Netmetrix Solutions S.L.
Av. de la Industria 53, Planta 2, Oficina 3
28108 Alcobendas - Madrid
CIF: B86773736
Netmetrix Solutions S.L.
Av. de la Industria 53, Planta 2, Oficina 3
28108 Alcobendas - Madrid
CIF: B86773736
New Supplier Survey: Access the link to fill out the questionnaire
Legal Notice
NETMETRIX SOLUTIONS S.L., a Spanish company responsible for the website https://www.netmetrix.es/, hereinafter the CONTROLLER, makes this document available to users, intended to comply with the obligations set forth in Law 34/2002, of July 11, on Information Society Services and Electronic Commerce (LSSICE), as well as to inform all users of the website regarding the conditions of use.
Any person accessing this website assumes the role of a user, committing to the observance and rigorous fulfillment of the provisions herein, as well as any other applicable legal provision. NETMETRIX SOLUTIONS S.L. reserves the right to modify any type of information that may appear on the website, without any obligation to give prior notice or inform users of said obligations, with publication on this website being understood as sufficient.
1. IDENTIFYING DATA
Domain name: www.netmetrix.es
Company name: NETMETRIX SOLUTIONS S.L.
Tax ID (CIF): B86773736
Postal Address: Av de la Industria, 53, 28108 Alcobendas, Madrid
Telephone: 916 613 147
e-mail: lopd@netmetrix.es
Registered in the Commercial Registry: Madrid, Volume 31316, Folio 18, Sheet Number M563673, entry: 10
2. INTELLECTUAL AND INDUSTRIAL PROPERTY RIGHTS
The website, including but not limited to its programming, editing, compilation, and other elements necessary for its operation, designs, logos, text, and/or graphics, are the property of the CONTROLLER or, if applicable, it holds a license or express authorization from the authors. All website content is duly protected by intellectual and industrial property regulations and registered in the corresponding public registries. Regardless of the purpose for which they were intended, total or partial reproduction, use, exploitation, distribution, and commercialization require prior written authorization from the CONTROLLER. Any use not previously authorized is considered a serious breach of the author's intellectual or industrial property rights.
3. DISCLAIMER OF LIABILITY
The CONTROLLER is exempt from any type of liability derived from the information published on its website, provided that this information has been manipulated or introduced by a third party external to it.
4. LINK POLICY
From the website, it is possible to be redirected to content on third-party websites. Since the CONTROLLER cannot always control the content introduced by third parties on their respective websites, it does not assume any type of responsibility for said content. In any case, it will proceed to the immediate withdrawal of any content that could contravene national or international legislation, morality, or public order, proceeding to the immediate withdrawal of the redirection to said website and informing the competent authorities of the content in question. The CONTROLLER is not responsible for the information and content stored, including but not limited to, in forums, chats, blog generators, comments, social networks, or any other means that allows third parties to publish content independently on the CONTROLLER's website. However, and in compliance with the provisions of articles 11 and 16 of the LSSICE, it makes itself available to all users, authorities, and security forces, actively collaborating in the withdrawal or, where appropriate, blocking of all content that may affect or contravene national or international legislation, the rights of third parties, or morality and public order. If a user considers that there is any content on the website that could be susceptible to this classification, please notify the website administrator immediately. This website has been reviewed and tested to ensure it functions correctly. In principle, correct operation can be guaranteed 365 days a year, 24 hours a day. However, the CONTROLLER does not rule out the possibility of certain programming errors, or that force majeure events, natural disasters, strikes, or similar circumstances may occur that make access to the website impossible.
5. IP ADDRESSES
The website's servers may automatically detect the IP address and domain name used by the user. An IP address is a number automatically assigned to a computer when it connects to the Internet. All this information is registered in a duly registered server activity file that allows the subsequent processing of the data in order to obtain only statistical measurements that allow knowing the number of page impressions, the number of visits made to the web servers, the order of visits, the access point, etc.
6. APPLICABLE LAW AND JURISDICTION
For the resolution of all controversies or issues related to this website or the activities carried out on it, Spanish legislation will apply, to which the parties expressly submit, with the Courts and Tribunals of Madrid being competent for the resolution of all conflicts arising from or related to its use.
Privacy Policy
Through this Privacy Policy, Netmetrix aims to demonstrate its commitment to complying with the regulations and laws arising from the processing of information necessary for providing its services and the use of Information and Communication Technologies. In particular, Netmetrix expresses its commitment to complying with regulations focused on the protection of personal data. In this regard, the following are considered the main reference frameworks:
- Regulation (EU) 2016/679 of the European Parliament and of the Council of 27 April 2016 on the protection of natural persons with regard to the processing of personal data and on the free movement of such data (GDPR).
- Organic Law 3/2018, of December 5, on the Protection of Personal Data and guarantee of digital rights.
- This statement applies to any website, application, product, software, or service belonging to Netmetrix that is linked to it (collectively, our "Services"). Occasionally, a service will be linked to a separate privacy statement that will list the specific privacy practices of that service.
- This policy may be updated periodically, so we urge you to access and review it. If we make changes that we consider significant, we will inform you through a notice on the relevant services or by communicating with you through other means such as email.
1. ABOUT US
Netmetrix is a company dedicated to the testing of network equipment, systems, and service platforms; commercialization, design, and automation services; technological training; commercialization of equipment for the military, industrial, and aerospace sectors; and located at Av. de la Industria, 53, 28108 Alcobendas, Madrid. Our address for notifications, communications, and contact is Av. de la Industria, 53, 28108 Alcobendas, Madrid. Additionally, Netmetrix has provided the following email address for communications and notifications related to the processing of information and personal data, including the exercise of the rights indicated in this Policy: lopd@netmetrix.es. If you want more information, click here: https://www.netmetrix.es
2. INFORMATION AND PERSONAL DATA WE COLLECT
Personal information refers to any information that relates to an identified or identifiable natural person. An identifiable natural person is one who can be identified, directly or indirectly, particularly by reference to an identifier such as a name, an identification number, location data, an online identifier, or one or more factors specific to the physical, physiological, genetic, mental, economic, cultural, or social identity of that person. We collect, store, and process the information (and particularly personal data) necessary to provide our services. Specifically, the information we collect is:
- Information from our clients necessary for our services of testing network equipment, systems, and service platforms; commercialization, design, and automation services; technological training; commercialization of equipment for the military, industrial, and aerospace sectors, including identifying and contact information, academic and professional information, and economic and banking data required to provide our services and for our operational and business purposes. Although most of this information is business-related, it may include personal data, mainly concerning the contact personnel of our client companies.
- For the proper development of these services of testing network equipment, systems, and service platforms; commercialization, design, and automation services; technological training; commercialization of equipment for the military, industrial, and aerospace sectors; Netmetrix personnel may have access to information and personal data contained in our client companies' files. In these cases, Netmetrix will commit to maintaining the confidentiality and security of this data, for which it will adhere to the necessary confidentiality commitments and external processing contracts.
- Upon requesting the consent of the interested parties, Netmetrix may send commercial or informational communications, such as a NEWSLETTER, by email, for which the identifying and contact data provided directly by the interested party will be used. These mailings will specifically indicate the appropriate mechanisms to disable the reception of these communications.
- Similarly, we will collect information, including personal data (mainly identifying and contact), through our website, whenever you register for events advertised through it, or whenever the contact or information request mechanisms are used.
We also collect personal information from third parties such as our partners, collaborators, service providers, and publicly available websites to offer services that we believe may be of interest to you and to help us maintain data accuracy and to offer and improve the services. Additionally, our servers, logs, and other technologies automatically collect certain information to help us administer, protect, and improve our services, analyze their use, and enhance the user experience.
Internally, Netmetrix collects, stores, and processes the personal data of its employees and collaborators, which is necessary to maintain the employment relationship with the workers and to comply with legal obligations in this matter.
3. HOW WE PROTECT INFORMATION AND PERSONAL DATA
At Netmetrix, we have a strong commitment to the security of the information we handle and to complying with the legal requirements that apply to us. In this sense, to ensure the confidentiality, availability, and integrity of both the information we handle (and, in particular, personal data), and the systems, networks, applications, and databases used for its processing, at Netmetrix: we periodically carry out risk assessments associated with information security and personal data protection, analyzing our risk situation and defining action plans accordingly. An Information Security and Data Protection Policy has been defined that is mandatory for all parties involved in the processing of information. Procedures for Access Control, Systems and Communications Security, Incident and Security Breach Management, and Information Backup have been developed. Awareness and training actions have been developed to ensure compliance with these policies and procedures. If, as a user or affected party, you detect any security incident or breach, or any vulnerability that could be affected, Netmetrix makes the following address available to the affected parties: lopd@netmetrix.es, through which you can make the communications that are considered appropriate or necessary for improving the security of our information and systems.
4. RIGHTS OF DATA SUBJECTS
Netmetrix has enabled the necessary means to comply with the right to information and to obtain consent where necessary to ensure the lawfulness of the processing of personal data. At the time of obtaining or collecting the information, Netmetrix undertakes to inform the affected parties about the identity of the controller, the purpose, possible communications or transfers, and the possibility of exercising the rights established in the regulations. Netmetrix recognizes and guarantees the possibility of exercising the rights of access, rectification, erasure, opposition, restriction of processing, and portability, as established by data protection regulations.
You as an interested or affected party can:
RIGHT OF ACCESS: Obtain confirmation as to whether or not your data is being processed and, if so, you will have the right to access the following information regarding the processing of your data: the purposes of the processing; the categories of personal data concerned; the recipients or categories of recipients to whom the personal data may be communicated; the envisaged period for which the personal data will be stored; the existence of the right to request the rectification, erasure, or opposition of data, or the restriction of processing; the right to lodge a complaint with a supervisory authority; where the personal data have not been obtained from the interested party, any available information about their origin; the existence of automated decisions, including profiling, and significant information about the logic applied, as well as the importance and the envisaged consequences of such processing for the interested party. When personal data are transferred to a third country or to an international organization, the interested party shall have the right to be informed of the appropriate safeguards pursuant to Article 46 relating to the transfer.
RIGHT TO ERASURE: Obtain the erasure of your data when any of the following circumstances occur (provided that the data does not fall under any of the exceptions contemplated in the regulations: that they are data of general interest, necessary for compliance with a legal obligation, or for exercising the right to freedom of expression...): the personal data are no longer necessary for the purpose for which they were collected; the interested party withdraws the consent given for the processing of the data; the interested party objects to the processing and no other legitimate grounds for the processing prevail; the personal data have been processed unlawfully; the personal data must be erased for compliance with a legal obligation that may be established.
RIGHT TO RECTIFICATION: Modify inaccurate, erroneous, or incomplete data.
RIGHT TO PORTABILITY: Receive from Netmetrix the personal data concerning you and transmit them to another data controller when: the lawfulness of the processing is based on the consent of the interested party or on the fulfillment of a contract; the processing is carried out by automated means.
RIGHT TO OBJECT: Object to the processing of personal data concerning you based on the fulfillment of purposes of public interest, or of legitimate interest for the controller.
RIGHT TO RESTRICTION OF PROCESSING: Obtain from the data controller the restriction of the processing of data when any of the following conditions is met: the interested party contests the accuracy of the personal data, for a period that allows the controller to verify the accuracy of the same; the processing is unlawful and the interested party opposes the erasure of the personal data and requests instead the restriction of their use; the controller no longer needs the personal data for the purposes of the processing, but the interested party needs them for the formulation, exercise, or defense of claims; the interested party has objected to the processing by virtue of the right of opposition. For the exercise of these rights, Netmetrix has provided the email address: lopd@netmetrix.es, through which you can contact the organization to request the exercise of the rights that the regulations recognize. Similarly, these can be exercised through the postal address indicated in the first section. For the proper exercise of these rights, we urge you to use as a reference the templates and models for the exercise of rights that can be found on the website of the Spanish Data Protection Agency (https://www.aepd.es/). Furthermore, we inform you of the possibility, in the event that you consider that your rights have been violated, or that action has not been taken appropriately with respect to the rights requests that you may have made, to file the corresponding complaint with the Spanish Data Protection Agency, which you can contact through the electronic headquarters accessible from its website (https://www.aepd.es/).
5. WHAT INFORMATION WE COMMUNICATE OR TRANSFER
As a general rule, at Netmetrix, we only communicate personal data to third parties, or provide them with access to it, in cases necessary for the proper provision of the requested service, to comply with legal, tax, and corporate obligations, or for the development of certain processes or activities of the organization in a subcontracted manner (Access to Data by Third Parties). In particular, we carry out communications and exchanges of information with banking entities, based on the services provided, to manage the collection and billing of the services provided, the management of payments to service providers, or in compliance with legal, tax, and public duties. Likewise, in compliance with these public duties, communications are made to other administrative bodies, such as Social Security or the Tax Administration. On the other hand, at Netmetrix, we establish agreements, alliances, or collaborations with other entities that provide us with certain services or that collaborate in the development of certain activities, and they may have access to the personal data that we manage. This is the case, for example, of tax and labor consultancies that are granted access to the personal data of our workers for payroll management, compliance with public duties, or prevention of occupational risks. In addition, we have certain subcontracted services that we rely on for the provision and development of our services. This is mainly the case for external hosting (housing) or web hosting services. For the provision of these services, the corresponding external processing contracts have been signed, ensuring compliance with the requirements of the regulations. It may be the case that these services are provided or require the intervention of entities or systems hosted in third countries. Netmetrix ensures that, in cases where international data transfers are required, these are made to countries that demonstrate a level of security comparable to that of European regulations. In this regard, the adequacy decisions of the European Data Protection Committee will be considered, or, failing that, certificates, corporate standards, contractual clauses, or any other recognized mechanism that certifies an adequate level of protection.
6. HOW LONG WE RETAIN INFORMATION
As a general rule, at Netmetrix, we only retain information and personal data for the time necessary to fulfill the purpose for which the data was obtained, as well as to address possible claims or responsibilities that arise as a result of the processing of the data. In general, once the provision of the service has ended, the data is blocked, and no further processing is carried out on it other than keeping it available to Public Administrations, Judges, and Courts, for the attention of possible responsibilities arising from the processing, during their statute of limitations, after which it must be canceled. On the other hand, to determine the data retention periods, Netmetrix considers local laws, contractual obligations, and the expectations and requirements of our clients. When we no longer need personal information, we delete or destroy it securely.
7. INTELLECTUAL AND INDUSTRIAL PROPERTY
The content of the services and websites of Netmetrix, including its structure, design, texts, source code, as well as the logos, trademarks, and other distinctive signs that appear on it, are the property of Netmetrix or its collaborators or third-party associates, and are protected by the corresponding intellectual and industrial property rights. Likewise, the images, videos, sounds, audios, and other graphic elements contained in the portals are protected by the corresponding rights. Therefore, by virtue of the provisions of Articles 8 and 32.1 of the Intellectual Property Law, it is expressly prohibited to copy, reproduce, publish, or alter any content of the Netmetrix websites without its prior authorization.
Netmetrix authorizes the total or partial reproduction of the texts and content provided by the portal, provided that the following conditions are met:
- The integrity of the content, documents, or graphics is maintained.
- Netmetrix is expressly cited as the source and origin of those.
- The purpose and aim of such use is compatible with the activity of Netmetrix.
- No commercial use is intended, with their distribution, public communication, or transformation being expressly prohibited.
- The User undertakes to respect the Intellectual and Industrial Property rights owned by Netmetrix. They may view the elements of the portal and even print, copy, and store them on their computer's hard drive or on any other physical medium as long as it is solely and exclusively for their personal and private use. The User must refrain from deleting, altering, evading, or manipulating any protection device or security system that was installed on the Netmetrix pages.
8. GENERAL CONDITIONS OF USE AND RESPONSIBILITIES
The Netmetrix websites are intended to facilitate, to the general public, knowledge of the activities that this company carries out and the products and services it provides, as well as to offer the possibility of contracting certain services. Likewise, the partial or total provision of certain services contracted by clients is permitted. The use of any of these websites implies the express and full acceptance of the conditions set forth herein, without prejudice to those particular conditions that may apply to some of the specific services offered through the site. In order to keep the information published on the portals updated, their content may be modified, corrected, deleted, or added at any time, so it will be convenient to check their validity or accuracy by consulting official sources. Likewise, this privacy policy may be subject to change, correction, or modification, in order to keep it adequate to the needs of the organization, as well as to current regulations.
a. Responsibility for the operation of the Web
Netmetrix cannot guarantee the absence of errors in accessing the Web services or in their content, although Netmetrix will develop the necessary mechanisms to reduce these scenarios and correct or update them as quickly as possible. Likewise, Netmetrix cannot be held responsible for possible errors, interferences, or interruptions of the service that may arise from causes such as computer viruses, telephone or network breakdowns, disconnections, and other types of failures caused by reasons beyond the control of the Web owner. Netmetrix reserves the right to temporarily suspend the operation of the web services, at any time, whenever necessary for maintenance, repair, updating, or improvement tasks. Likewise, Netmetrix reserves the right to deny or withdraw access to the portal and/or the services offered without prior notice, at its own request or that of a third party, to those users who breach these General Conditions of Use. On the other hand, Netmetrix is not responsible for the content that may be published by users or by any third party through the forums, comments, or social networks associated with the websites, although Netmetrix will provide the necessary means to remove this type of content and to guarantee compliance with applicable legislation, as well as respect for the rights of those affected and public order. If users detect any content that affects in this sense, it is recommended that they contact Netmetrix as soon as possible, through the means provided.
b. Responsibility for links
The links contained in our web services may lead to external web services, managed by third parties, in order to facilitate user access to related information or resources. Netmetrix does not manage, review, or can be held responsible for the content, operation, or information of the websites to which it directs, with which it maintains no relationship. Netmetrix cannot be held responsible for the damages and losses that may arise from these linked pages. Likewise, the inclusion of these external connections will not imply any type of association, merger, or participation with the connected entities.
c. Responsibility of users
- The User guarantees that the Personal Data provided to Netmetrix (where necessary) are true and is responsible for communicating any modification thereof. The user will be solely responsible for any damage or harm, direct or indirect, that may be caused to the file manager or to any third party due to the completion of the forms with false, inaccurate, incomplete, or outdated data.
- The User undertakes to use the Website, the content, and services in accordance with the Law, this Legal Notice, good customs, and public order. Likewise, the User undertakes not to use the Website or the services provided through it for purposes contrary to the content of this Legal Notice, or for illicit purposes or those harmful to the interests and/or rights of third parties, such as: disseminating content or propaganda of a racist, xenophobic, pornographic-illegal nature, in apology of terrorism or that violates human rights; causing damage to the physical and logical systems of Netmetrix, its suppliers, or third parties; introducing or disseminating computer viruses or any other physical or logical systems that are likely to cause the aforementioned damage; trying to access and, where appropriate, use the accounts of other users and modify or manipulate their messages.
- The User expressly undertakes not to destroy, alter, disable, or in any other way, damage the data, programs, or electronic documents and others found on this Website, as well as not to hinder its proper functioning.
- Likewise, the User undertakes not to hinder the access of other users to the service through the massive consumption of computer resources through which the owner of the Web provides the service, as well as to carry out actions that damage, interrupt, or generate errors in said systems.
- The User undertakes not to introduce programs, viruses, macros, applets, ActiveX controls, or any other logical device or sequence of characters that may cause errors on the web.
9. APPLICABLE LAW AND JURISDICTION
The resolution of conflicts, controversies, or claims that may arise from the web services to which this privacy policy refers will be governed by the provisions of Spanish legislation. Netmetrix will submit to the Judges, Courts, and jurisprudence of the city of Madrid (Spain), unless otherwise agreed with the consumer/user.
Cookies Policy
1. INFORMATION ABOUT COOKIES
Due to the entry into force of the relevant amendment to the "Law on Information Society Services" (LSSICE) established by Royal Decree 13/2012, it is mandatory to obtain the express consent of the user on all web pages that use non-essential cookies, before the user browses them.
2. WHAT ARE COOKIES?
Cookies and other similar technologies such as local shared objects, flash cookies, or pixels, are tools used by Web servers to store and retrieve information about their visitors, as well as to ensure the proper functioning of the site. Through the use of these devices, the Web server can remember some data concerning the user, such as their preferences for viewing the pages of that server, name and password, products that interest them most, etc.
3. COOKIES AFFECTED BY REGULATIONS AND EXEMPT COOKIES
According to the EU directive, the cookies that require the user's informed consent are analytics, advertising, and affiliate cookies. Technical cookies and those necessary for the operation of the website or the provision of services expressly requested by the user are exempt.
4. WHAT TYPES OF COOKIES ARE THERE?
Regarding the types of cookies, there are five main groups:
Analytics cookies: collect information about the use of the website.
Social cookies: are those necessary for external social networks.
Affiliate cookies: allow tracking of visits from other websites with which the website establishes an affiliation contract (affiliate companies).
Advertising and behavioral cookies: collect information about the user's preferences and personal choices (retargeting).
Technical and functional cookies: are those strictly necessary for the use of the website and for the provision of the contracted service.
5. LIST AND DESCRIPTION OF THE COOKIES WE USE ON THE WEBSITE
The table published below provides a schematic list of the cookies we use on our website
6. SOCIAL MEDIA COOKIES
Some pages on our websites allow you to share our content on social networks like Facebook, Twitter, Google, etc. Sometimes we post videos from sites like YouTube. These websites set their own cookies, which we do not control. You may wish to check their websites to learn more about their cookie policies. More information on social media cookies:
https://es-es.facebook.com/about/privacy/cookies
https://www.youtube.com/howyoutubeworks/policies/community-guidelines/
https://www.linkedin.com/legal/privacy-policy
7. FROM YOUR BROWSER, YOU CAN
Avoid the use of Cookies by disabling the use of Cookies in your browser and deleting the Cookies stored in your browser associated with this website. You can carry out this action to avoid the use of Cookies at any time. Avoid the download of cookies during your browsing session by selecting the "Incognito browsing" option or similar (although the next time you want to access your personal account, you will have to log in), which also means that other session variables will not be stored. Delete cookies. To delete the cookies linked to your personal account at NETMETRIX SOLUTIONS, you must do so from the domain https://www.netmetrix.es/
8. REVOKING CONSENT TO INSTALL COOKIES AND HOW TO DELETE COOKIES FROM YOUR BROWSER
Chrome
- Select the Tools icon.
- Click on Settings.
- Click on Show Advanced Options.
- In the "Privacy" section, click on Content settings.
To delete cookies: Click on All cookies and site data.
To prevent cookies from being stored: Click on Clear browsing data (empty the Cache).
Close and restart the browser. For more information about Chrome, click here: http://support.google.com/chrome/answer/95647?hl=en
Internet Explorer. Version 11
- Select Tools | Internet Options.
- Click on the General tab.
- In the "Browsing history" section, click on Delete browsing history on exit.
- Select Delete files.
- Select Delete cookies.
- Click on Delete.
- Click on OK.
- Close and restart the browser. For more information about Internet Explorer, click here: http://windows.microsoft.com/es-419/windows7/how-to-manage-cookies-in-internet-explorer-9
Firefox. Version 18
- Select Firefox | History | Clear Recent History.
- Next to "Details," click the down arrow.
- Select the following checkboxes: Cookies, Cache, Active Logins.
- Using the "Time range to clear" drop-down menu, select Everything.
- Click on Clear Now.
- Close and restart the browser. You can accept or reject cookies individually in the Firefox Preferences, in the History section available under Tools > Options > Privacy. For more information about Mozilla Firefox, click here: https://www.mozilla.org/es-ES/privacy/websites/#cookies
Safari Version 5.1
- Select the Safari icon / Edit | Reset Safari.
- Select the following checkboxes: Clear history, Remove all website data.
- Click on Reset.
- Close and restart the browser. For more information about Safari, click here: http://support.apple.com/kb/PH5042
Opera
Options – Advanced – Cookies. The cookie options control how Opera handles them and therefore their acceptance or rejection. For more information about Opera, click here: http://help.opera.com/Linux/10.60/es-ES/cookies.html
Other browsers: Consult the documentation for the browser you have installed.
9. Information on data transfers to third countries made by NETMETRIX SOLUTIONS
NETMETRIX SOLUTIONS does not perform international transfers to third countries.
In the case of third parties, you can find information on transfers to third countries that, where applicable, are carried out by the third parties identified in this cookie policy in their respective policies (see the link to third-party cookie policies in the table).
10. PROFILING NETMETRIX SOLUTIONS does not perform profiling.
11. REGARDING THE REST OF THE INFORMATION REQUIRED BY ARTICLE 13 OF THE GDPR We refer you to the Privacy Policy of NETMETRIX SOLUTIONS. (link to the Privacy Policy).
Terms of Contract
The contracting of services or the sale of products cannot be carried out electronically; therefore, it is necessary to contact a sales representative to access pricing information and to request quotes based on the characteristics of each client.
Quality and Environmental Policy
NETMETRIX, dedicated to providing services for testing networks, systems, and service platforms; sales and automation services; military, industrial, and aerospace hardware; and technological training, has decided to implement Quality strategies aligned with the Business. The ultimate goal is to continuously improve customer satisfaction and service, with the general objective of creating a more innovative, responsive, and efficient service that facilitates clients' activities, ensuring its availability and enhancing their degree of satisfaction.
Therefore, the company is committed to the implementation, maintenance, and continuous improvement of a Quality System. Implemented in all its areas of activity, this system ensures compliance with client specifications, the company's own standards, and legally established requirements, guaranteeing effective and efficient planning, execution, and control of service management.
The Management of NETMETRIX commits to providing the necessary resources to achieve the following strategic objectives:
- Establish the continuous improvement of the quality system's effectiveness by planning, executing, reviewing, and enhancing the Management System, always considering the organization's internal and external context.
- Orient Quality towards the Satisfaction of all our clients (and interested parties). This will require facilitating the commitment and active participation of all personnel involved in the company's activities, by training and raising awareness in service management so that they are knowledgeable of and comply with the defined management activities.
- Identify and analyze the existing needs surrounding the provision of services and develop the necessary services to provide an adequate response to those needs.
- Develop a complete and efficient management structure that regulates the conditions under which the organization, within the established scope, must carry out its activities to respect the established requirements.
- Develop all necessary measures to ensure that the quality levels offered by the services are maintained over time, promoting continuous improvement and the effectiveness of the management system. This includes adequately managing any incidents that may arise, making error prevention a fundamental aspect.
- Periodically establish a set of objectives and indicators for service management to allow for adequate monitoring of both the service levels offered and the management activities developed around them. This also includes paying maximum attention to technological evolution and potential improvements that new technologies may offer.
- Comply with all applicable legal, normative, and regulatory requirements, as well as those established in the services or others that are applicable.
- Allocate the necessary resources and means to develop services with the quality levels required by clients, maintaining an appropriate balance between cost and benefit.
- Develop our projects by considering the environmental aspects of each activity, focusing on efficient use of energy resources, promoting the use of renewable energies, using environmentally friendly and sustainable materials, and ensuring the efficient use of water.
- Protect the environment and prevent pollution directly resulting from our work, ensuring the safety and well-being of people, reducing waste generation, and managing its efficiency throughout its entire life cycle.
- This Policy provides the frame of reference for the continuous improvement of the Management System. It is communicated to the entire Organization through the organization's document management system and its publication on information panels. It is reviewed annually for its continued suitability and extraordinarily when special situations and/or substantial changes in the Management System occur. It is available to the general public.
According to ISO 9001/14001, the scope of the Netmetrix system is as follows:
- Testing of networks, systems, and service platforms
- Monitoring of networks, systems, and service platforms
- Commercialization, design, and services in automation and AI agents
- Technology and soft skills training
- Commercialization of equipment for critical infrastructures (military, industrial, energy, and aerospace)
Delivery Policy
Within the services provided by Netmetrix, projects for the new installation of applications developed by the entity shall be considered as deliveries. In order to guarantee that these services are provided properly and in accordance with the subscribed service level agreements, a Delivery Policy has been established based on the following principles:
- Planning and supervision of deliveries, ensuring their deployment into production within the deadlines agreed upon with clients or set by the applicable service level agreements.
- Ensuring the proper functioning of the systems, by carrying out the relevant tests on the exact contents considered in the delivery.
- Implement the deliveries of new versions.
SECURITY POLICY
1. Approval and entry into force
This Information Security Policy is effective from the date of signature and until it is replaced by a new Policy.
2. Organizational Mission
NETMETRIX, to achieve its objectives, assumes its commitment to information security, committing to the proper management of it, in order to offer all its stakeholders the greatest guarantees regarding the security of the information used. These systems must be managed diligently, taking appropriate measures to protect them against accidental or deliberate damage that may affect the availability, integrity, or confidentiality of the information processed or the services provided.
The objective of information security is to guarantee the quality of information and the continuous provision of services, acting preventively, monitoring daily activity, and reacting quickly to incidents. ICT systems must be protected against rapidly evolving threats with the potential to affect the confidentiality, integrity, availability, intended use, and value of information and services.
To defend against these threats, a strategy is required that adapts to changes in environmental conditions to guarantee the continuous provision of services. This implies that departments must apply the minimum security measures required by the National Security Framework (ENS), as well as continuously monitor service delivery levels, follow and analyze reported vulnerabilities, and prepare an effective response to incidents to guarantee the continuity of the services provided. The different departments must ensure that ICT security is an integral part of each stage of the system life cycle, from its conception to its withdrawal from service, including development or acquisition decisions and operational activities. Security requirements and funding needs must be identified, both for the products it develops and its associated services, as well as for the base software acquired from third parties. Departments must be prepared to prevent, detect, react to, and recover from incidents, in accordance with Article 8 of the ENS (Article 8. Prevention, detection, response, and conservation).
3. Scope
This policy applies to all ICT systems of the entity and to all members of the organization involved in Services and Projects destined for the public sector that require the application of ENS, without exception. “Information Security Management System applied to:
- Testing of networks, systems, and service platforms.
- Monitoring of networks, systems, and service platforms.
- Commercialization, design, and automation services.
- Technological training.
- Commercialization of equipment for critical infrastructures (military, industrial, energy, and aerospace)
4. Objectives
Based on all the above, Management establishes the following information security objectives:
- Provide a framework to increase resilience to provide an effective response.
- Ensure the rapid and efficient recovery of services in the face of any physical disaster or contingency that could occur and put the continuity of operations at risk.
- Prevent information security incidents to the extent technically and economically viable, as well as mitigate information security risks generated by our activities.
- Guarantee the confidentiality, integrity, availability, authenticity, and traceability of information.
5. Regulatory framework
One of the objectives must be to comply with applicable legal requirements and any other requirements to which we subscribe in addition to the commitments acquired with customers, as well as their continuous updating. To this end, the legal and regulatory framework in which we carry out our activities is:
- REGULATION (EU) 2016/679 OF THE EUROPEAN PARLIAMENT AND OF THE COUNCIL of 27 April 2016 on the protection of natural persons with regard to the processing of personal data and on the free movement of such data.
- Organic Law 3/2018, of December 5, on the Protection of Personal Data and guarantee of digital rights.
- Royal Legislative Decree 1/1996, of April 12, Intellectual Property Law.
- Law 2/2019, of March 1, which modifies the revised text of the Intellectual Property Law, approved by Royal Legislative Decree 1/1996, of April 12, and which incorporates into the Spanish legal system Directive 2014/26/EU of the European Parliament and of the Council, of February 26, 2014, and Directive (EU) 2017/1564 of the European Parliament and of the Council, of September 13, 2017.
- Royal Decree 311/2022, of May 3, which regulates the National Security Framework (ENS)
- Law 34/2002 of July 11, on Information Society Services and Electronic Commerce (LSSI).
- Law 40/2015, of October 1, on the Legal Regime of the Public Sector.
- Law 39/2015, of October 1, on the Common Administrative Procedure of Public Administrations.
6. Development
In order to achieve these objectives, it is necessary to:
- Improve continuously our information security system.
- Identify potential threats, as well as the impact on business operations that such threats, if materialized, may cause.
- Preserve the interests of its main stakeholders (customers, shareholders, employees, and suppliers), reputation, brand, and value-creation activities.
- Work jointly with our suppliers and subcontractors in order to improve the provision of IT services, service continuity, and information security, which results in greater efficiency of our activity.
- Evaluate and guarantee the technical competence of the personnel, as well as ensure their proper motivation for their participation in the continuous improvement of our processes, providing appropriate training and internal communication so that they develop good practices defined in the system.
- Guarantee the correct state of the facilities and appropriate equipment, so that they correspond to the activity, objectives, and goals of the company.
- Guarantee a continuous analysis of all relevant processes, establishing the pertinent improvements in each case, based on the results obtained and the objectives established. The management of our system is entrusted to the Chief Information Security Officer (CISO) and the system will be available in our information system in a repository, which can be accessed according to the access profiles granted according to our current access management procedure. Structure our management system so that it is easy to understand.
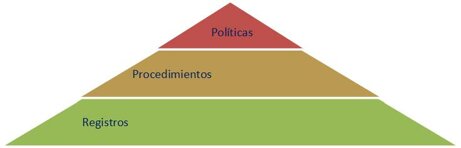
Structure our management system so that it is easy to understand. Our management system has the following structure:
Netmetrix Solutions S.L. © 2025 All rights reserved | Privacy Policy - Other-Policies
Netmetrix Solutions S.L. © 2025 All rights reserved | Privacy Policy - Other-Policies
7. Security Organization
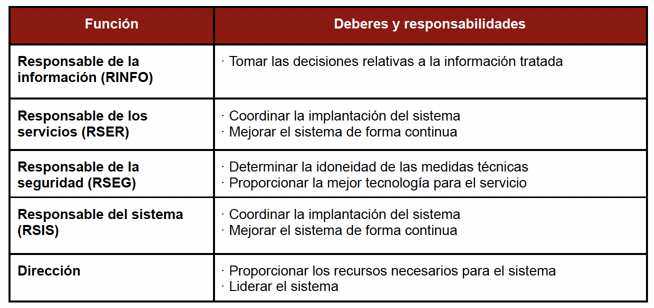
The essential responsibility lies with the General Management of the organization, as it is responsible for organizing functions and responsibilities and providing appropriate resources to achieve the ENS objectives. Managers are also responsible for setting a good example by following established security standards. These principles are assumed by Management, which provides the necessary means and provides its employees with sufficient resources for compliance, translating them and making them public knowledge through these Security Policies. This definition of duties and responsibilities is completed in the job profiles and in the system documents Register of responsible persons, roles, and responsibilities.
CONFLICT RESOLUTION: Differences of criteria that could lead to a conflict will be handled within the Security Committee and the criteria of the General Management will prevail in all cases.
8. Security Committee
The procedure for their designation and renewal will be ratification in the security committee. The committee for the management and coordination of security is the body with the greatest responsibility within the information security management system, so that all the most important decisions related to security are agreed upon by this committee. The members of the information security committee are:
- Information Owner
- Service Owner
- Security Officer
- System Officer
Company Management These members are designated by the committee, the only body that can appoint, renew, and dismiss them. The security committee is an autonomous, executive body with autonomy for decision-making and does not have to subordinate its activity to any other element of our company. The organization of Information Security is developed in the document complementary to this Security Organization Policy. This policy is complemented by the rest of the policies, procedures, and documents in force to develop our management system.
9. Risk Management
All systems subject to this Policy must perform a risk analysis, evaluating the threats and risks to which they are exposed.
This analysis is reviewed regularly:
- at least once a year;
- when the information handled changes;
- when the services provided change;
- when a serious security incident occurs;
- when serious vulnerabilities are reported.
For the harmonization of risk analyses, the ICT Security Committee will establish a reference assessment for the different types of information handled and the different services provided. The ICT Security Committee will promote the availability of resources to meet the security needs of the different systems, promoting horizontal investments. To carry out the risk analysis, the risk analysis methodology developed in the Risk Analysis procedure will be taken into account.
10. Personnel Management
All members of NETMETRIX have the obligation to know and comply with this Information Security Policy and the Security Regulations, and it is the responsibility of the ICT Security Committee to provide the necessary means so that the information reaches those affected. All members of NETMETRIX will attend an ICT security awareness session at least once a year. A continuous awareness program will be established to serve all members of the organization, particularly new additions. Persons with responsibility for the use, operation, or administration of ICT systems will receive training for the safe handling of the systems to the extent they need it to perform their work. Training will be mandatory before assuming a responsibility, whether it is their first assignment or a change of job position or responsibilities within it.
11. Professionalism and security of human resources
This Policy applies to all NETMETRIX personnel and external personnel who perform tasks within the company. HR will include information security functions in employee job descriptions, inform all personnel they hire of their obligations regarding compliance with the Information Security Policy, manage Confidentiality Commitments (NDAs) with personnel, and coordinate user training tasks regarding this Policy.
The Security Management Officer (RGS) is responsible for monitoring, documenting, and analyzing reported security incidents, as well as communicating with the Information Security Committee and information owners.
The Information Security Committee will be responsible for implementing the necessary means and channels for the Security Management Officer (RGS) to handle incident reports and system anomalies. The Committee will also be aware of, supervise the investigation, monitor the evolution of the information, and promote the resolution of information security incidents.
The Security Management Officer (RGS) will participate in the preparation of the Confidentiality Commitment to be signed by employees and third parties performing functions at NETMETRIX, in advising on the sanctions to be applied for non-compliance with this Policy, and in the handling of information security incidents.
All NETMETRIX personnel are responsible for reporting information security weaknesses and incidents that are detected in a timely manner.
Professionalism of human resources:
- Determine the necessary competence of personnel to carry out work that affects Information Security.
- Ensure that people are competent based on appropriate education, training, or experience.
- Demonstrate through documented information that personnel competence in Information Security is necessary.
The objectives of controlling personnel security are:
- Reduce the risks of human error, implementation of irregularities, misuse of facilities and resources, and unauthorized handling of information.
- Explain security responsibilities at the recruitment stage and include them in the agreements to be signed and verify compliance during the performance of the employee's tasks.
- Ensure that users are aware of information security threats and concerns and are trained to support the organization's Information Security Policy in the course of their normal tasks.
- Establish confidentiality commitments with all personnel and users outside the information processing facilities.
- Establish the necessary tools and mechanisms to promote the communication of existing security weaknesses, as well as incidents, in order to minimize their effects and prevent their recurrence.
12. Authorization and control of access to Information Systems
The control of access to information systems aims to:
- Prevent unauthorized access to information systems, databases, and information services.
- Implement security in user access through authentication and authorization techniques.
- Control security in the connection between the NETMETRIX network and other public or private networks.
- Review critical events and activities carried out by users in the systems.
- Raise awareness of their responsibility for the use of passwords and equipment.
- Guarantee information security when using laptops and personal computers for remote work.
13. Protection of facilities
The objectives of this policy regarding the protection of facilities are:
- Prevent unauthorized access, damage, and interference to the headquarters, facilities, and information of NETMETRIX
- Proteger el equipo de procesamiento de información crítico de NETMETRIX, colocándolo en áreas protegidas y protegido por un perímetro de seguridad definido, con las medidas de sicurezza e controles de acceso adecuados. Likewise, consider its protection during transfer and when remaining outside protected areas, for maintenance or other reasons.
- Control environmental factors that could harm the proper functioning of the computer equipment that houses NETMETRIX information.
- Implement measures to protect information handled by personnel in offices, in the normal course of their usual tasks.
- Provide protection proportional to the identified risks. This Policy applies to all physical resources related to NETMETRIX information systems: facilities, equipment, cabling, files, storage media, etc. It should be noted that in the case of NETMETRIX, all development, quality environments, etc., are located externally in secure hosting, so only laptops and peripherals must be protected locally.
- The Security Management Officer (RGS), together with the Information Owners, as appropriate, will define the physical and environmental security measures for the protection of critical assets, based on a risk analysis, and will supervise their application.
- They will also verify compliance with physical and environmental security provisions. Those responsible for the different departments will define the physical access levels of NETMETRIX personnel to the restricted areas under their responsibility. Information Owners will formally authorize off-site work with business information for NETMETRIX employees when they deem it appropriate. All NETMETRIX personnel are responsible for compliance with the clean screen and desk policy for the protection of information related to daily work in the offices.
14. Acquisition of products
Different departments must ensure that ICT security is an integral part of each stage of the system life cycle, from its conception to its withdrawal from service, including development or acquisition decisions and operational activities. Security requirements and funding needs must be identified and included in the planning, in the request for offers, and in tender specifications for ICT projects. On the other hand, information security will be taken into account in the acquisition and maintenance of information systems, limiting and managing change.
15. Security by default
NETMETRIX considers it strategic for the entity that processes integrate information security as part of their life cycle. Information systems and services must include security by default from their creation to their withdrawal, including security in development and/or acquisition decisions and in all operational activities, establishing security as an integral and transversal process.
16. System integrity and updating
NETMETRIX is committed to guaranteeing the integrity of the system through a change management process that allows the control of the updating of physical or logical elements through prior authorization for their installation in the system. This evaluation will be carried out mainly by the technical management, which will evaluate the impact on the security of the system before making the changes and will control in a documented manner those changes that are evaluated as important or with implications for the security of the systems. Through periodic security reviews, the security status of the systems will be evaluated in relation to manufacturer specifications, vulnerabilities, and updates that affect them, reacting diligently to manage the risk in view of their security status.
17. Protection of information stored and in transit
NETMETRIX establishes protection measures for the Security of Information stored or in transit through insecure environments. Laptops, peripheral devices, information media, and communications over open networks or with weak encryption will be considered insecure environments.
18. Prevention of interconnected information systems
NETMETRIX establishes protection measures for Information Security, especially to protect the perimeter, in particular, if it connects to public networks, especially if they are used entirely or mainly for the provision of electronic communication services available to the public. In any case, the risks derived from the interconnection of the system, through networks, with other systems will be analyzed, and their point of union will be controlled. Electronic connections available to the public.
19. Activity logs
NETMETRIX will record user activities, retaining the information necessary to monitor, analyze, investigate, and document improper or unauthorized activities, allowing the person acting to be identified at all times.
The main objectives of Incident Management are:
- Establish a detection and reaction system against harmful code.
- Disponer de procedimientos de gestión de incidentes de seguridad y de debilidades detectadas en los elementos del sistema de información.
- Estos procedimientos cubrirán los mecanismos de detección, los criterios de clasificación, los procedimientos de análisis y resolución, así como los cauces de comunicación a las partes interesadas y el registro de las actuaciones.
- Este registro se emplea para la mejora continua de la seguridad del sistema.
- Guarantee that IT services return to optimal performance.
- Reduce potential risks and impacts that the incident may cause.
- Velar por la integridad de los sistemas en el caso de un incidente de seguridad.
- Comunicar el impacto de un incidente tan pronto como se detecte para activar la alarma; y implementar un adecuado corporate communication plan.
- Promover la eficiencia empresarial.
20. Continuity of activity
NETMETRIX, with the objective of guaranteeing the continuity of activities, establece medidas para que los sistemas dispongan de copias de sicurezza e establece mecanismos necesarios para garantizar la continuidad de las operaciones, en caso de pérdida de los medios habituales de trabajo.
21. Continuous improvement of the security process
NETMETRIX establece un proceso de mejora continua de la seguridad de la información aplicando los criterios y metodologia establecida en el Esquema Nacional de Seguridad (ENS).
If you need to access the full policies, please request them at: ISO_NMX@netmetrix.es